

Authentication
Contentrain Studio supports three sign-in methods. Any of them creates your account and a personal workspace on first sign-in. All authentication flows are handled through the provider/adapter pattern, so the underlying implementation can be swapped without changing any application code.
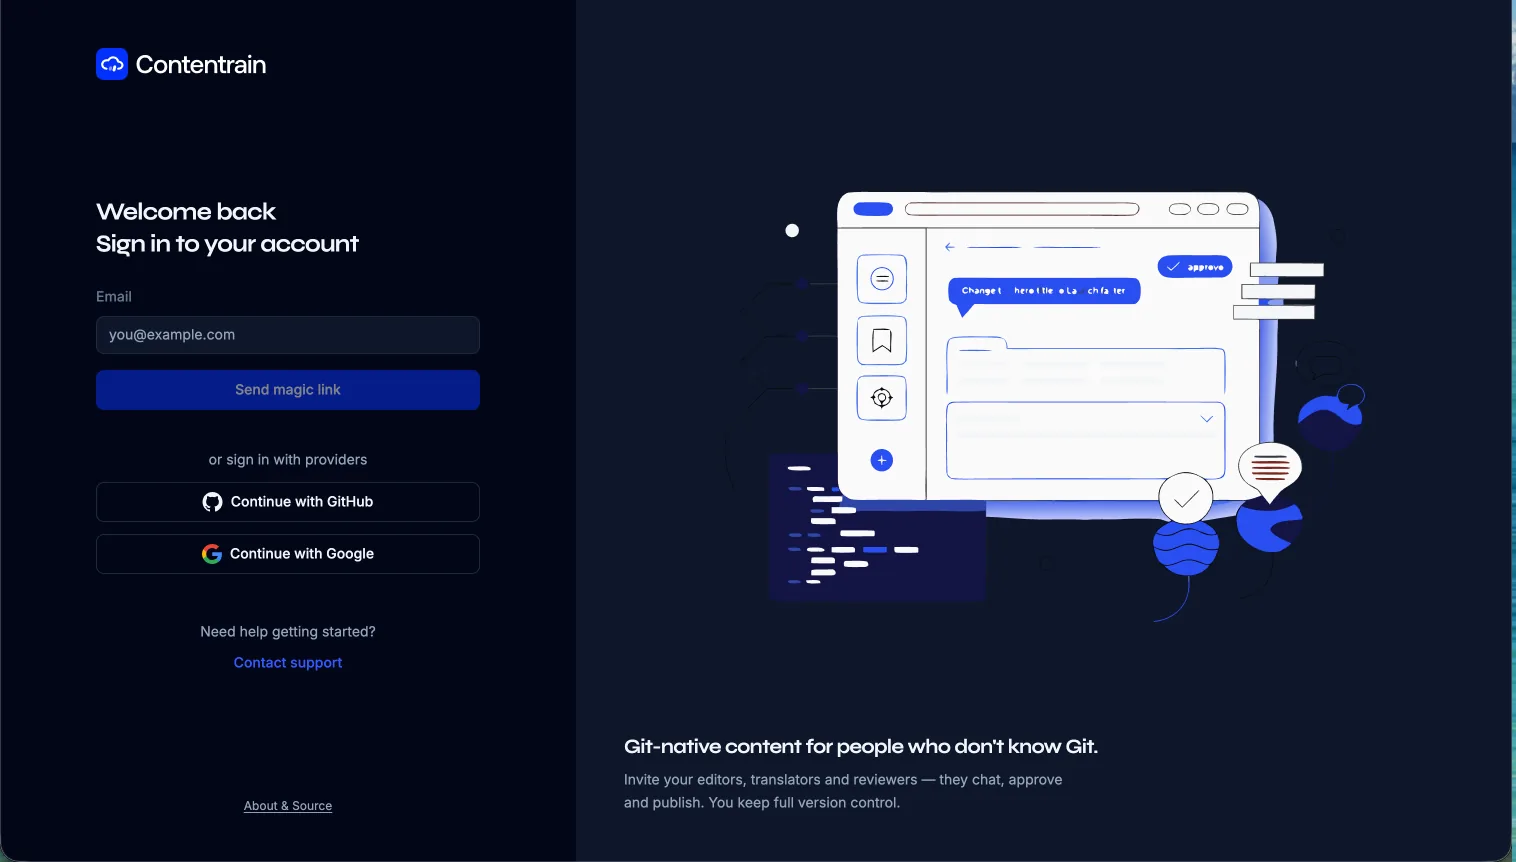
Sign-In Methods
GitHub OAuth
GitHub OAuth is the supported way to connect repositories. Studio reaches your repositories through the GitHub App, and signing in with GitHub lets Studio verify that you have access to the installation you attach to a workspace.
Best for: Developers and anyone who connects repositories and installs the GitHub App.
Flow:
- Click Continue with GitHub on the login page
- GitHub redirects you to authorize the Contentrain app
- Studio creates your account and a personal workspace
- You are redirected back to Studio
TIP
If this is your first login, Studio automatically creates a personal workspace for you. You can create additional team workspaces later.
Google OAuth
Google OAuth provides a convenient sign-in option if you prefer a Google account over GitHub.
Best for: Content editors, reviewers, and anyone who prefers a Google account over GitHub.
Flow:
- Click Continue with Google on the login page
- Google redirects you to authorize the Contentrain app
- Studio creates your account and a personal workspace (or signs you in if you already have one)
- You are redirected to your workspace
TIP
Signing in with Google for the first time self-registers, exactly like GitHub — Studio creates your account and a personal workspace automatically. No invitation is required. (If your Google email matches an account you were already invited under, Studio links to it instead of creating a duplicate.)
Magic Link
Magic Link is a passwordless email-based authentication method. Studio sends a one-time login link to your email address.
Best for: People who prefer not to use OAuth providers, or organizations that restrict third-party OAuth. No invitation is required.
Flow:
- Click Sign in with Email on the login page
- Enter your email address
- Click Send magic link
- Check your inbox and click the link
- Studio verifies the token and signs you in
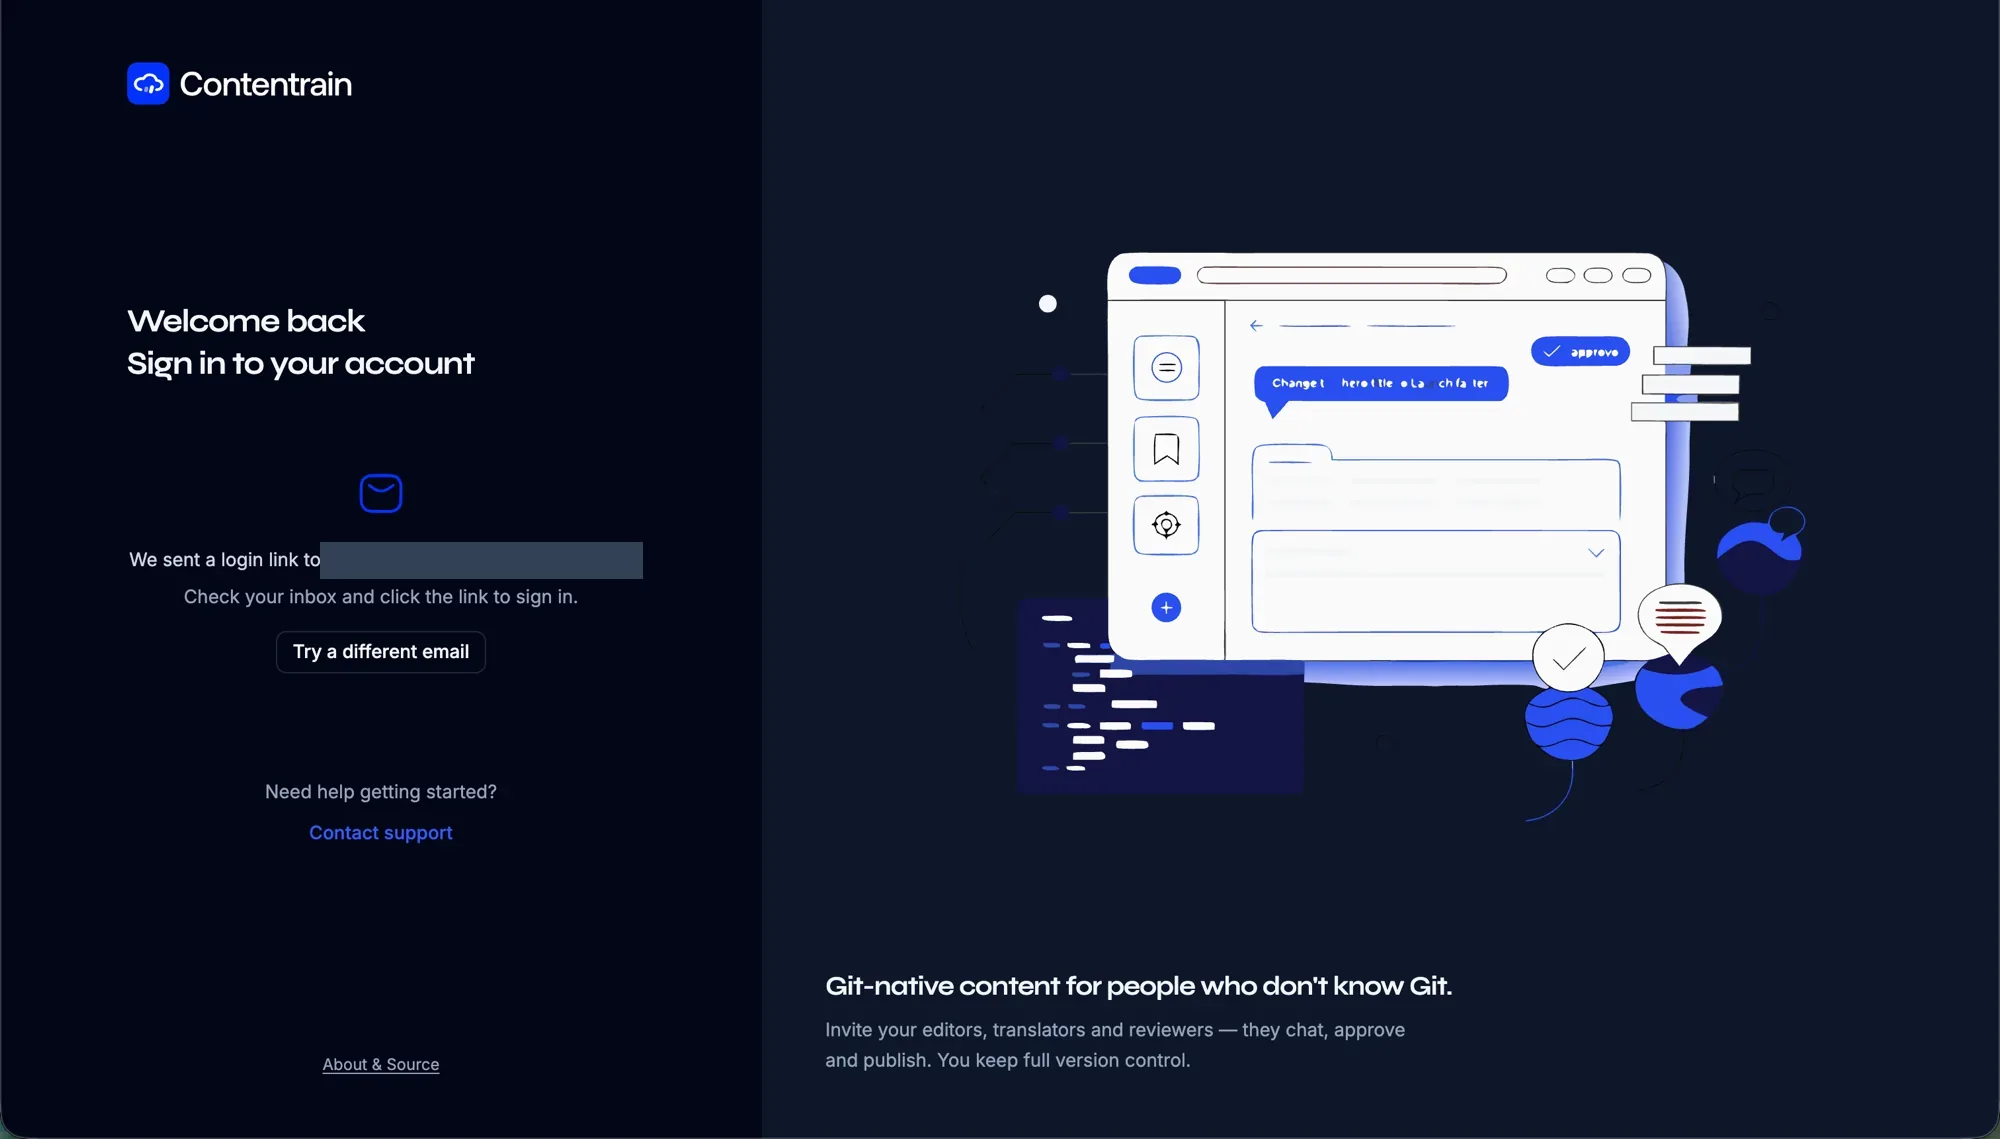
After the magic link is sent, you will see a confirmation screen with the email address. You can click Try a different email to start over.
TIP
Magic links expire after a short period. If your link has expired, return to the login page and request a new one.
When to Use Which Method
| Method | Who | Why |
|---|---|---|
| GitHub OAuth | Developers, anyone connecting repositories | The supported path for installing the GitHub App and connecting repositories |
| Google OAuth | Editors, reviewers, teammates | Quick sign-in with an existing Google account; self-registers like GitHub |
| Magic Link | Anyone | Passwordless, no third-party OAuth dependency; self-registers like the OAuth methods |
Auth Callback
After any OAuth flow (GitHub or Google), Studio redirects to /auth/callback. This page:
- Validates the OAuth state parameter (CSRF protection)
- Exchanges the authorization code for a session
- Creates or updates the user profile
- Redirects to the workspace dashboard
You do not need to interact with the callback page directly — it handles the handoff automatically.
Session Management
Studio uses encrypted, HTTP-only cookies for session management:
- Encryption: AES-256 encrypted session data
- Storage: Server-side
httpOnlycookie (not accessible to JavaScript) - Auto-refresh: Sessions are automatically refreshed on activity
- Expiration: A session ends after 7 days without activity; the window restarts whenever the session is refreshed
Signing Out
You can sign out at any time with the Sign out icon button next to your name at the bottom of the sidebar. (Clicking your name or avatar opens your account settings instead.) This clears your session cookie and redirects you to the login page.
Account Deletion
Studio supports full account deletion from the user settings page at /settings:
- Click your name or avatar at the bottom of the sidebar to open account settings (the sidebar Settings link opens workspace settings, not your account)
- Open the Account tab
- In the Danger Zone, click Delete My Account
- Confirm by typing your email address
WARNING
Account deletion is permanent. All your data, including workspaces you own, is removed. It is refused until you transfer ownership of any team workspace that still has other members, and until any owned workspace with a still-billing subscription is cancelled. See Account Settings.
Security Considerations
- CSRF protection: OAuth flows use a
stateparameter stored server-side in an encrypted,httpOnlycookie and validated on callback - No password storage: Studio never stores passwords — all authentication is delegated to OAuth providers or magic link tokens
- Provider isolation: Authentication logic is contained within the auth provider adapter. No Supabase-specific code exists outside the provider layer
- Role enforcement: Authentication identity is separate from authorization. Roles and permissions are enforced at the API level regardless of sign-in method
Next Steps
- Workspaces — Create and manage your team workspaces
- Team Management — Invite members and assign roles
- Quickstart — Get started with your first project